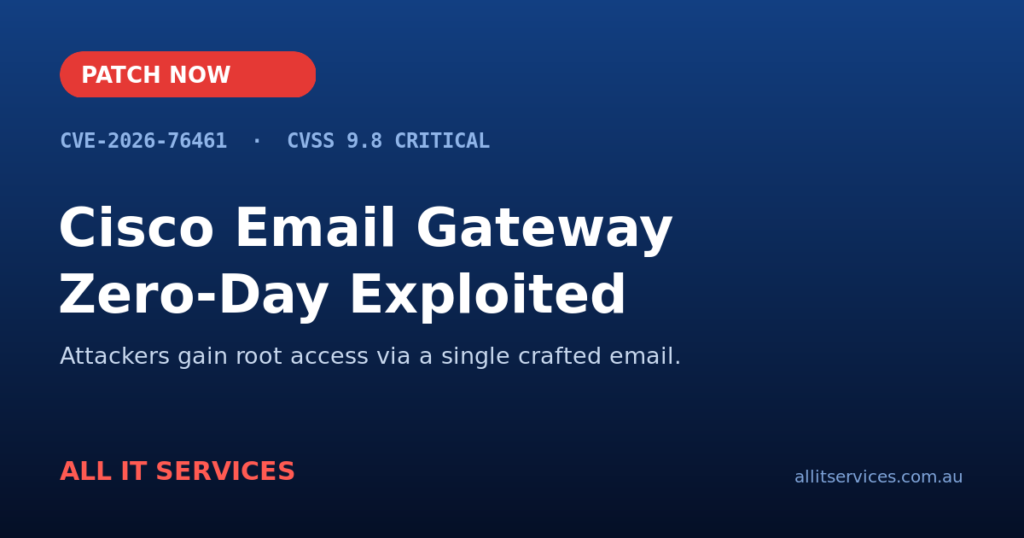
Cisco Email Gateway Zero-Day Under Attack: Patch Now
If your business runs a Cisco Secure Email Gateway appliance, physical or virtual, there's a critical zero-day being actively exploited right now. A single crafted email is enough for an attacker to get root access, no clicks needed.
Cisco confirmed the flaw, tracked as CVE-2026-76461 and rated 9.8 out of 10, after BleepingComputer reported active exploitation on 15 September 2026. The bug sits in the appliance's email parsing logic: malicious SQL statements hidden in a message can trigger command execution with root privileges, no login required. Shadowserver is already tracking roughly 400 exposed devices being probed. In our experience, appliances like this one are usually set-and-forget, racked once and left alone until something breaks, which is exactly what attackers go looking for first.
Cisco has released fixes: 15.5.5-0141 for AsyncOS 15.5 and earlier, 16.0.4-302 for 16.0, and 16.5.0-780 for 16.5, through Cisco's own security advisory. There's no workaround, so patching is the only real fix. If you manage your own appliance, check mail_logs for suspicious SQL statements and review firewall logs for unusual outbound traffic. If All IT looks after your email security, we're already working through the patch schedule for affected clients, but if you're unsure whether your gateway is covered, get in touch today.
Written by Caleb Attard, Head of Business Operations, All IT Services. All IT is a Sydney-based managed IT provider supporting hospitality, not-for-profit and wealth management businesses across Australia.
Frequently Asked Questions
Not sure if your email gateway is patched?
All IT Services helps Australian businesses find and close gaps like this one before attackers do. Get a free check of your exposure today.
Related Guide
Cybersecurity for Sydney SMBs
Explore our complete guide to protecting your business from cyber threats.
Read the Full Guide →